Tabletop exercises offer IT service providers (ITSPs) a unique opportunity to demonstrate their value as strategic partners—guiding clients through crisis decision-making, reinforcing security awareness and identifying actionable improvements. These exercises not only build resilience but also deepen trust, positioning MSPs as essential allies in navigating today’s evolving threat landscape. But facilitating such an event can be more of an art than a science.
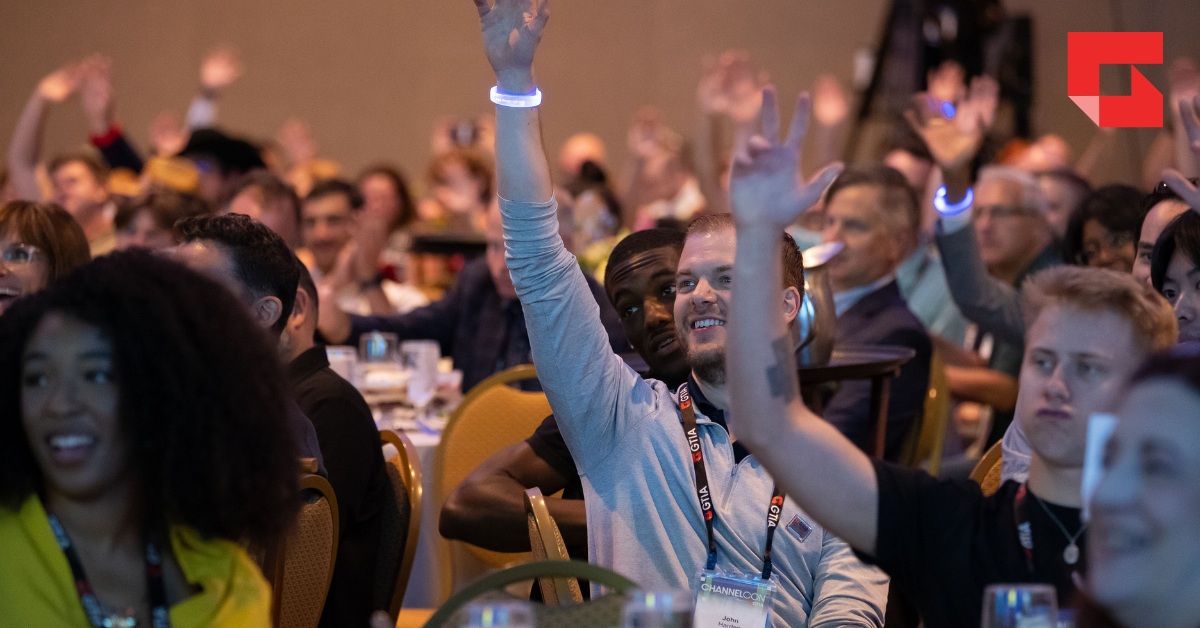
At ChannelCon 2025, Nett Lynch, chief information security officer, Kraft & Kennedy, Inc., Tanja Omeragic, director of technical sales for cybersecurity, ConnectWise and Natalie Suarez, cyber ambassador, Suarez Consulting led a room full of people through the steps of conducting a tabletop exercise designed to simulate the pressures of decisions faced during a cybersecurity incident.
The underlying sentiment? You fight the way you train.
“Everybody has a plan until you get punched in the face,” Lynch said. “So, the more times you get punched in the face, the more you know how to react.”
Your Training Goals
When a cyber incident occurs, you can be sure two things will be present: Stress and adrenaline. Your goal is to learn how to manage those factors. This is best done by first ensuring the tabletop exercise is business focused.
“Sit in the seat of your client so you can adjust the way you conduct a tabletop exercise in a way that resonates better with them.” Lynch said. “You can customize these to be as meaningful as possible, so they turn into business decisions. We need all the decision makers at the table.”
Related Content: Building Effective Tabletop Exercises
During the ChannelCon session, the group broke out into 10 tables where different scenarios from the GTIA Cybersecurity Guidebook for ITSPs: Tabletop Exercises to Build Customer Resilience and Preparedness were assigned. Each table included a facilitator to mimic the role of the ITSP, and each participant was given a persona to play. The persona detailed the individual’s role within the organization but also noted a few personal biases and feelings—an all too realistic component at any table.
The Tabletop Exercise Playbook
The guidebook offers a practical framework for ITSPs to lead their teams—and clients—through exercises that simulate real-world cyber incidents. From ransomware and phishing to insider threats and deepfake hiring attacks, each scenario is designed to uncover vulnerabilities, clarify roles and strengthen response strategies.
Scenario 1: Data Breach
This tabletop exercise simulates a data breach, allowing you to walk through the real-world challenges, understand the potential impact on your business and identify how your team, alongside your MSP, would respond.
Goal for the client participants: To understand the end-to-end implications of a data breach, assess your organization’s readiness and clarify roles and responsibilities during a crisis.
Scenario 2: Social Engineering Attack
This exercise simulates a highly deceptive social engineering attack, focusing on a fraudulent financial transfer. It’s designed to explore how your organization would respond to such a sophisticated scam, focusing on prevention, detection and mitigation.
Goal for the client participants: To understand the vulnerabilities to social engineering, assess your financial controls and communication protocols, and clarify roles and responsibilities in preventing and responding to financial fraud.
Scenario 3: Business Email Compromise
This exercise simulates a business email compromise (BEC) attack, a highly effective and costly type of fraud. It’s designed to help clients understand how a seemingly simple email can lead to significant business disruption and financial loss.
Goal for the client participants: To recognize the risks of social engineering and BEC, evaluate internal processes for handling sensitive information requests, and understand the coordinated response required when a key executive is compromised.
Scenario 4: Ransomware via IoT Device
This exercise simulates a severe ransomware attack, demonstrating how a seemingly small vulnerability can lead to catastrophic business disruption. It’s designed to help clients understand the progression of such an attack, the importance of proactive security measures and the critical role of a robust recovery plan.
Goal for the client participants: To understand the typical attack chain of ransomware, evaluate your organization’s preventative measures, assess your incident response and recovery capabilities, and identify key areas for strengthening your business’s resilience.
Scenario 5: Insider Threat
This exercise simulates a highly damaging scenario: A ransomware attack initiated by a disgruntled insider. It highlights how employee dissatisfaction, if unaddressed, can be exploited by external threat actors with catastrophic consequences.
Goal for the client participants: To recognize the early warning signs of insider threats, evaluate employee support systems and security monitoring, and understand the profound business impact of a combined insider-initiated ransomware attack.
Scenario 6: Credential Compromise
This exercise simulates a credential compromise stemming from employee password reuse across personal and business accounts. It’s designed to help clients understand how seemingly minor employee habits can lead to significant data breaches, the importance of robust security policies and the critical role of vigilant monitoring and swift action in partnership with your ITSP.
Goal for the client participants: To recognize the risks of password reuse, understand the implications of a compromised email system, evaluate current security policies and clarify the steps needed to prevent and respond to credential-based attacks.
Scenario 7: Ransomware via Phishing
This exercise simulates a devastating ransomware attack that begins with a simple, yet highly effective, phishing email. It’s to help clients understand how vital employee training is in preventing such attacks, the rapid spread of ransomware and the critical importance of a robust recovery strategy.
Goal for the client participants: To recognize the significant role of employee security awareness, understand the progression of a ransomware attack, evaluate your organization’s recovery capabilities and identify key areas for strengthening your business’s resilience.
Scenario 8: Deepfake Hiring Attack
This exercise simulates a sophisticated and cutting-edge threat: A deepfake-enabled hiring attack, where a threat actor impersonates a legitimate candidate to gain insider access. This scenario is designed to help clients understand how advanced social engineering techniques can bypass traditional hiring processes, leading to the compromise of your most valuable assets.
Goal for the client participants: To recognize the emerging risks of deepfake technology in hiring, evaluate your current identity verification and onboarding processes, and understand the profound business impact of sensitive financial data theft.
Scenario 9: Supply Chain Attack
This exercise simulates a supply chain attack, where a trusted third-party software vendor inadvertently becomes the conduit for a cyberattack on your organization. It’s designed to help clients understand the hidden risks lurking in your software ecosystem, the profound impact when a trusted connection is compromised and the critical importance of vendor risk management and rapid response in partnership with your MSP.
Goal for the client participants: To recognize the vulnerability of the software supply chain, evaluate your third-party risk management practices and understand the cascading business impact when a critical vendor is compromised.
Scenario 10: Smartphone Compromise with SIM Swapping
This exercise simulates a sophisticated smartphone compromise through SIM swapping, a tactic where attackers take control of an executive’s phone number to gain access to critical business accounts. It’s designed to help clients understand how a personal mobile device can become a gateway to your most sensitive corporate data.
Goal for the client participants: To recognize the risks associated with mobile device security and SIM swapping, evaluate current MFA and account recovery policies, and understand the profound business impact of a compromised executive identity and stolen data.
Get your clients into their best cybersecurity shape.
GTIA Members: Download the GTIA Cybersecurity Guidebook for ITSPs: Tabletop Exercises to Build Customer Resilience and Preparedness on the Member Portal.
The GTIA North America Cybersecurity Interest Group is dedicated to helping tech businesses strengthen and build a robust cybersecurity strategy.