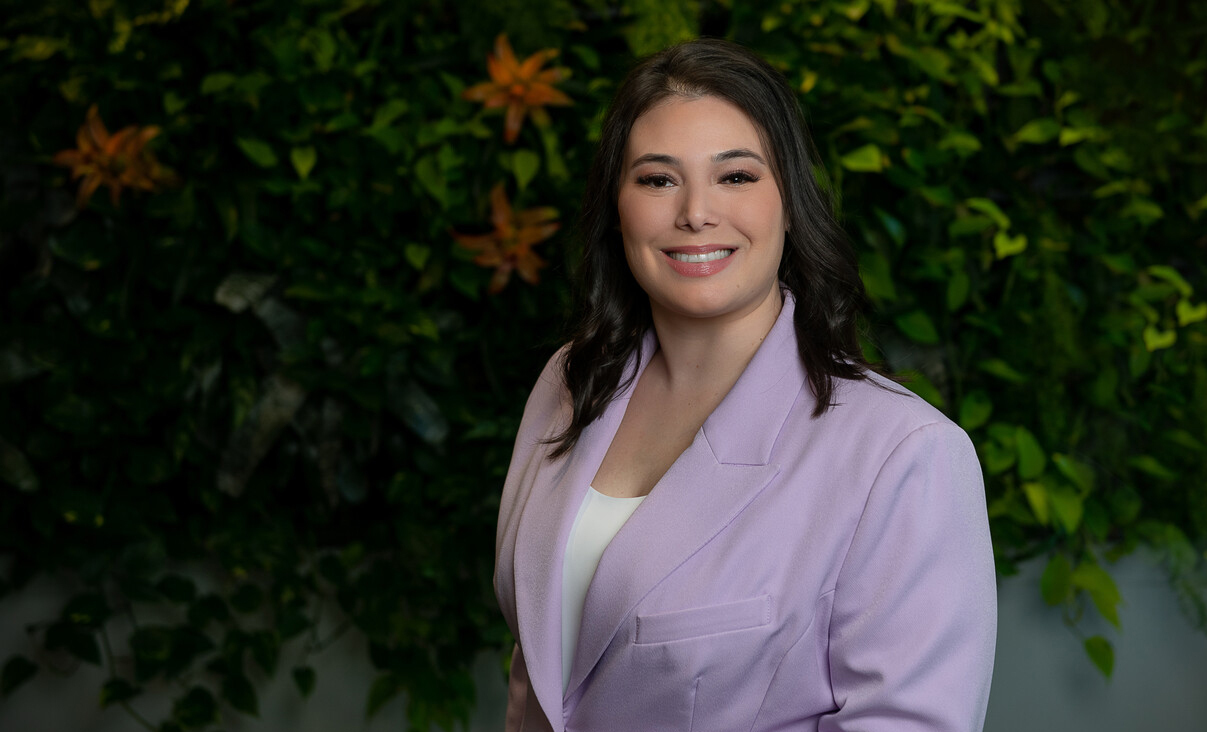
Technology has always been a big part of Alex Spigel’s life. Some of her earliest memories are playing with old computer equipment at the MSP business run by her father, Steve Rutkovitz. Since then, both her career and the business have developed significantly.
About 10 years ago, Alex and Steve founded Choice Cyber Solutions to help other MSPs and ITSPs stay cyber secure. She was named the GTIA Member of the Year for 2022-23 and also received the association’s 2023 Community Leadership Award. Along the way, she also became a mom, a recognized leader in the IT channel—and now a CEO. Spigel has been named to succeed her father, Steve Rutkovitz, at the helm of Choice Cyber Solutions, a position well-earned after nearly a lifetime in the making
We talked with Spigel about her career, her plans for growth, how GTIA and its members have helped her career, and what advice she has for ITSPs about the latest cybersecurity trends. Here’s what she had to say.
Congrats on the new role. What plans do you have for Choice Cyber Solutions?
My focus is on continuing to build Choice into a company that helps MSPs and their clients treat compliance as a core business requirement, not an afterthought—and use cybersecurity as the foundation that makes compliance sustainable and defensible.
From a leadership standpoint, that means being very intentional about structure, accountability, and execution. I believe strong outcomes come from clear ownership, disciplined processes, and empowering the right people to lead. As CEO, my role is to set direction, remove obstacles, and make sure our team has the clarity and support they need to deliver consistently at a high level.
Regulatory pressure, client accountability, and supply chain risk are increasing rapidly, and both MSPs and their clients are being held to higher standards. Our job is to bring order to that complexity. By applying compliance frameworks in a practical, personalized way, we help MSPs strengthen their own operations while enabling their clients to operate more securely and confidently.
We’re investing intentionally in our people, processes, and technical depth so we can scale responsibly without losing the white glove experience our partners and clients expect. Ultimately, my goal is to make compliance achievable, auditable, and defensible for MSPs and their clients—while building a company that’s disciplined, trusted, and built for long-term impact.
What has changed since being named GTIA Member of the Year in 2023?
Being named GTIA Member of the Year in 2023 was an incredible honor, but it also raised the bar for how I show up as a leader. Since then, I’ve become far more intentional—about how I listen, how I collaborate, and how I turn different perspectives into aligned action, especially when decisions have long-term compliance and risk implications.
Personally, I’ve changed a lot in the last few years. Becoming a working mom taught me something I didn’t fully appreciate before: energy is finite. I’ve learned to be much more selective about where I spend it, to set boundaries, and to say no when something doesn’t align. That focus has made me a more effective leader, not a less available one.
I’ve also become more grounded in my lane. Thought leadership is no longer about trying to cover everything—it’s about contribution. For me, that’s educating MSPs to “eat their own dog food” when it comes to governance and risk, and continuing to advocate for women in cybersecurity. Those are the areas where I can make the biggest impact, and I’ve learned that it’s okay—and necessary—to protect that focus.
GTIA also sharpened my view of where the industry is headed and reinforced the responsibility leaders have to elevate the broader ecosystem. I’m more confident in making long-term decisions, more disciplined about organization and follow-through, and more willing to bring in experts when I’m not the best person for the job—whether that’s consulting with a C3PAO for evolving CMMC requirements or investing in specialized talent on our team.
I still approach everything with the mindset of giving more than I receive. What’s changed is that I now do it with clearer boundaries, sharper focus, and a deeper commitment to building sustainable systems—not just solving the problem directly in front of me.
What have you learned from Steve that helped prepare you for this role?
Steve has been one of my greatest teachers in leadership, both as a partner and as a mentor. What I’ve learned most from him is that trust and consistency matter more than almost anything in this industry. He built his career as an MSP by doing the right thing—even when it was difficult or inconvenient—and by treating accountability and compliance as non-negotiable. That standard shaped how we built Choice from day one.
Over the past three-plus years, he’s also been incredibly intentional about preparing me for this role. That preparation wasn’t theoretical—it was hands-on. It meant being involved in tough conversations, long-term planning, and decisions where the right answer wasn’t always the easiest one. He reinforced the importance of operational discipline, clear ownership, and staying steady, especially when expectations rise or situations get uncomfortable.
Working side by side taught me that leadership isn’t about a title—it’s about showing up consistently, making hard decisions, and standing behind your team and your clients. Steve leads with integrity, and he expects the same from the people around him. Carrying that forward as CEO is something I take seriously, and it’s a big part of how I approach this next chapter at Choice.
How has GTIA and the community helped you—and Choice—prepare for what’s ahead?
GTIA—formerly CompTIA—has played a major role in shaping both my leadership approach and how Choice prepares for what’s ahead. Through volunteer leadership and deep involvement in initiatives like the GTIA Cybersecurity Trustmark and GTIA ISAO (Information Sharing and Analysis Organization) collaboration, I gained firsthand insight into how compliance standards are created, debated, and operationalized across the industry. That experience fundamentally changed how I think about compliance—not as a static requirement, but as a living system that has to evolve with risk.
Just as important has been the community itself. CompTIA, and now GTIA, surrounded me with peers who challenge assumptions, raise expectations, and aren’t afraid to have honest conversations about what’s working and what isn’t. That perspective—combined with the support I’ve received during both challenging and defining moments—has been invaluable personally and professionally, and it’s something I’m deeply grateful for.
That shared insight and collaboration directly influence how we lead at Choice. Being plugged into these conversations gives us early awareness of where regulatory and compliance expectations are heading, allowing us to anticipate change instead of reacting to it. It helps us design services that are practical, defensible, and aligned with where MSPs and their clients are going next—not where they’ve already been.
Ultimately, GTIA has reinforced my belief in leading with contribution first. Giving more than you receive, sharing knowledge openly, and building together as a community doesn’t just make individual leaders stronger—it makes the entire ecosystem more resilient. That mindset continues to guide both my leadership and Choice’s direction as we look ahead.
GTIA research shows many ITSPs still don’t offer cybersecurity as a core service. What advice do you have for those struggling to gain traction?
The biggest shift ITSPs need to make is recognizing that compliance has to come first. Cybersecurity can’t be a bolt-on product or a side offering—it needs to be built around a compliance framework that puts real structure around how you operate, manage risk, and protect both your business and your clients.
I’m deeply passionate about using compliance frameworks to bring order to cybersecurity. Without that structure, security efforts stay reactive and inconsistent. One of the most common mistakes I see is trying to secure clients before securing your own house. ITSPs are ultimately responsible for what happens on their watch, whether or not cybersecurity is formally offered. When an incident occurs—and it’s a matter of when, not if—clients will expect leadership, accountability, and answers.
The good news is you don’t have to do it alone. Power partnering with compliance and cybersecurity experts allows ITSPs to deliver mature, defensible services without overextending their teams. Being honest about where you need outside expertise isn’t a weakness—it’s smart leadership and risk management. Strong partners help you stay accurate, current, and confident as regulations and expectations evolve.
Start with the fundamentals: understand your clients’ compliance requirements, assess your own gaps, and build repeatable processes. Clients aren’t buying tools—they’re buying trust and guidance. ITSPs that lead with compliance, protect their own operations first, and leverage the right partners will gain traction, differentiate themselves, and build long-term credibility.
Interested in the GTIA Member of the Year Award? Learn more!