In a year marked by escalating digital threats as well as customer needs, dedication and attention to cybersecurity has never been more important for ITSPs—and, frankly, any organization.
Finding a partner that not only champions stronger, smarter defenses but also galvanizes support and awareness of cybersecurity is also critical in a community trying to ensure that everyone stays safe. But that’s exactly what Kristian Wright, co-founder and CEO of enhanced.io, does all day, every day.
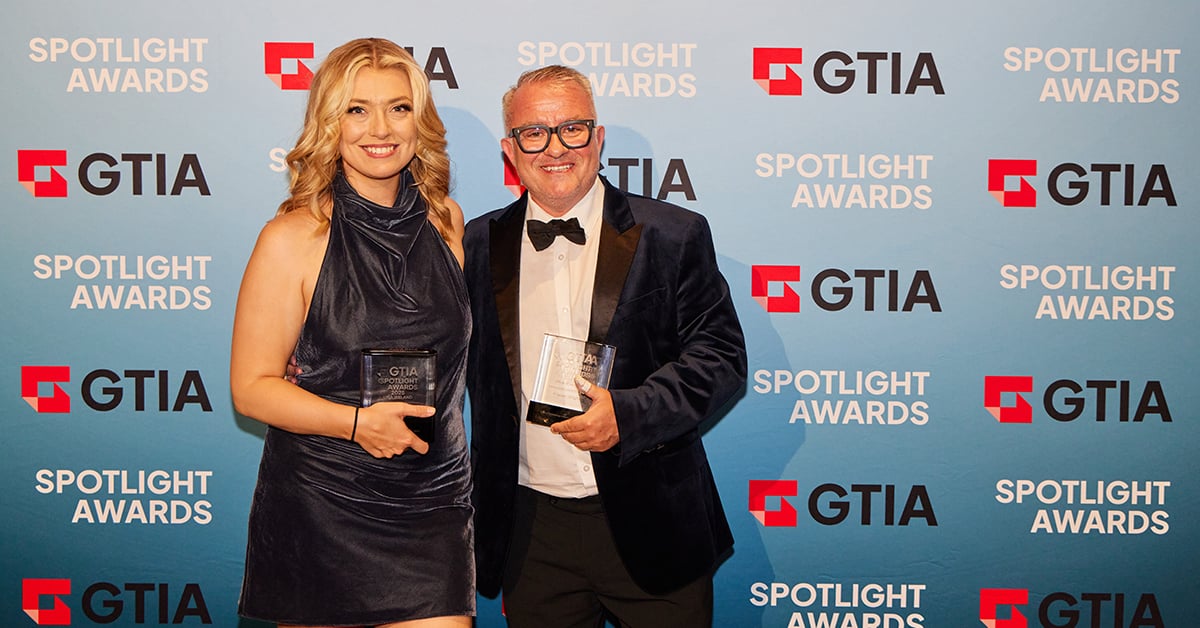
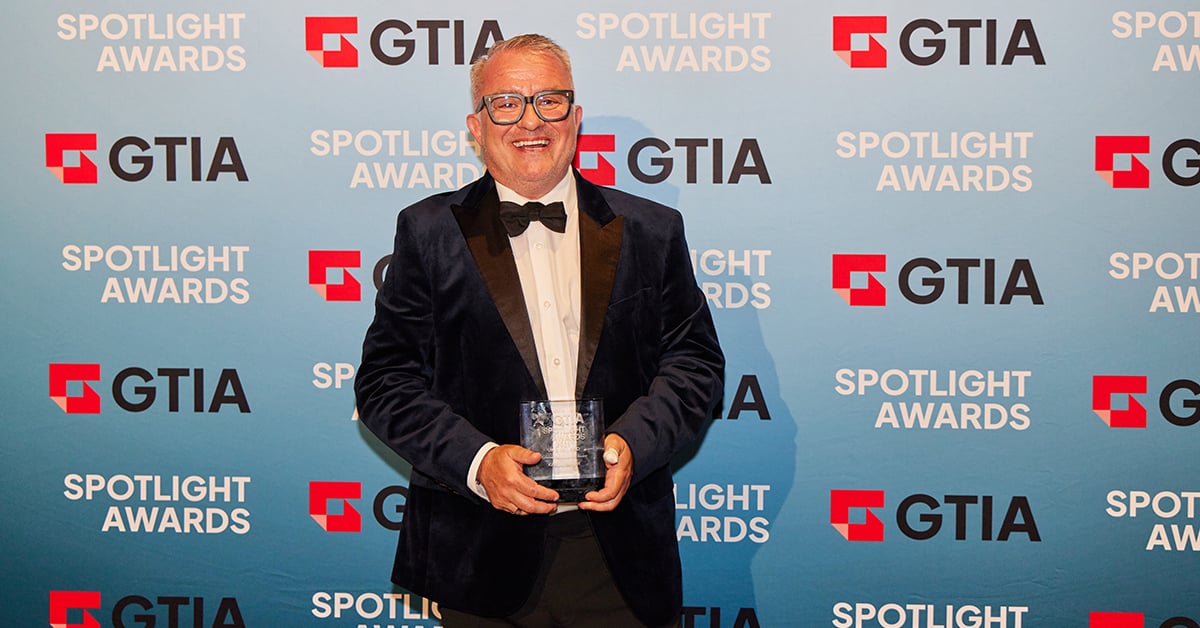
And it’s why Wright was chosen by GTIA member voters to receive the 2025 UK & Ireland Cybersecurity Leadership award, along with Brad Fraser, CEO of Infoprotect UK, for their outstanding commitment, leadership, passion and professionalism in their support for GTIA Cybersecurity Programs through active engagement and thought leadership around cybersecurity.
We asked Wright why cybersecurity advocacy is critical to safeguarding businesses and what advice he has for ITSPs to up their cyber resilience. Here’s what he had to say.
What does the GTIA UK & Ireland Cybersecurity Leadership Award mean to you?
Winning this award is a genuine honour. It’s a welcome acknowledgement of the persistent effort my team and I put into strengthening the digital landscape for ITSPs. Recognition from an organisation like GTIA reinforces our commitment to practical, shared cybersecurity standards across the channel. It means a great deal and motivates us to keep raising the bar.
What makes you such a tireless advocate for cybersecurity for ITSPs?
ITSPs are the backbone of countless businesses, yet they face unique and often overwhelming cybersecurity challenges. They’re prime targets, holding the keys to their clients’ kingdoms. I’m passionate about empowering them because their security directly impacts so many others. Seeing the tangible difference that knowledge and robust practices make—preventing breaches, protecting livelihoods—that’s what keeps me pushing for better, safer tech environments for everyone.
What is the biggest security challenge/risk ITSPs face today?
Fragmented visibility across multi-tenant, multi cloud and SaaS estates. Attackers thrive in the seams: Unmanaged identities, shadow admin rights, stale API tokens and inconsistent patch cadences across customer environments. Most ITSP tools were not built for that sprawl. Until we unify telemetry, normalise policy and continuously validate control coverage across tenants, we will keep discovering gaps the hard way—during incidents. Consolidated, actionable context beats yet another alert feed every time.
How are you working with GTIA to address those issues?
At a local level here in the UK we are collaborating through GTIA interest groups to map practical control tiers for service providers—good, better, best guidance aligned to realistic staffing levels. I have been contributing lessons from partner assessments and incident postmortems to help refine templates, playbooks and shared metrics. The aim: Reduce guesswork, improve cross provider comparability and give buyers clearer questions to ask. We are also encouraging peer reviews so smaller ITSPs can benchmark without fear of being sold to.
What advice do you have for ITSPs trying to up their cybersecurity game?
Start with scope and evidence. Inventory privileged identities, remote access paths and third-party integrations across all tenants—then close the riskiest gaps first. Adopt a minimum control profile you can prove (MFA everywhere, logging retention, patch SLAs, backup immutability). Automate the attestation of those controls and show results to customers quarterly. Finally, plug into the community: Shared indicators, tabletop drills and what went wrong exchanges move everyone forward faster than going it alone.