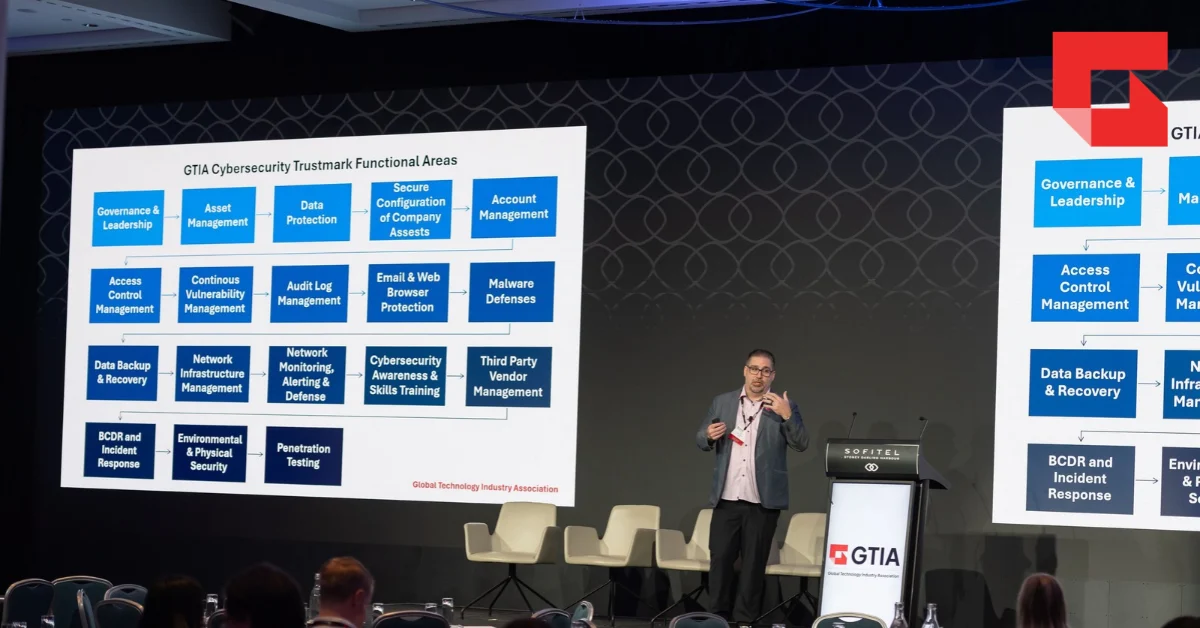
What is the GTIA Cybersecurity Trustmark? The GTIA Cybersecurity Trustmark is an independently assessed assurance for managed service providers (MSPs) and IT solution providers. It verifies that an organization meets or exceeds 18 controls and 177 safeguards drawn from CIS, NIST, HIPAA, NYDFS and ISO 27001. GTIA members prepare for assessment through the Trustmark Readiness Program.
Every IT service provider (ITSP) asks clients to take security seriously. The strongest ITSPs hold themselves to the same standard, and they prove it. Clients, prospects, insurers and auditors all want evidence that the partner managing their technology runs a secure business from the inside out.
The GTIA Cybersecurity Trustmark delivers that evidence. If you run a mature cybersecurity program today, or you are building toward one, the Trustmark Readiness Program gives you the structure, tools and community to get there. An independent assessment then confirms the work. The program is available exclusively to GTIA members.
Built for ITSPs by the IT Channel
GTIA Cybersecurity Programs staff and GTIA members built the Trustmark specifically for ITSPs and MSPs. The team reviewed risk and cybersecurity frameworks from around the world. They also gathered questionnaires from dozens of cyber insurance providers to learn what underwriters look for. Most of the safeguards ITSPs need already existed across many frameworks, and the Trustmark brings them together in one place.
The result is a standard of 18 domains and 177 safeguards. Its foundation is the Center for Internet Security (CIS) Critical Security Controls, supplemented by safeguards from NIST SP 800-171, NIST SP 800-53, HIPAA, the New York State Department of Financial Services (NYDFS) and ISO 27001. Every control earned its place through its relevance to ITSP businesses, and the standard applies in any geography.
The Trustmark is an assurance: Independent confirmation that your organization meets or exceeds a standard set by your industry peers. Your work carries over to other goals, too. The GTIA Cybersecurity Trustmark provides a strong foundation and crosswalk to other cybersecurity frameworks, giving you a head start on any others you'd like to tackle.
Josh Hohbein, information security lead at CentrexIT, explained why his team chose it: “The main reason we chose the GTIA Cybersecurity Trustmark is that we needed something with an MSP focus.”
The Readiness Program: Your Path to a Mature Security Posture
The Trustmark Readiness Program gives GTIA members 24 months of access to the Trustmark safeguards, guidance, implementation prompts, education, peer resources and GTIA industry partners. Everything you need to understand, embrace and implement best practices for risk and cybersecurity management lives in one program.
The Trustmark follows a true maturity model. It meets you where you are, confirms what you already do well and shows you which gaps to prioritize first. Smaller MSPs gain a clear starting point. Established security teams gain a deeper, more prescriptive layer of review.
Support is built into every stage of the program:
- Weekly Cyber Success calls
- Industry peer groups
- A dedicated space in the GTIA Cyber Hub to ask questions of peers, volunteers and program staff
- Platform Partners who help address safeguards across control domains
- Guidance from GTIA members who have already achieved the Trustmark
- Your member rep and the GTIA Cybersecurity Programs team
When you are ready, a CREST-accredited assessor verifies your work at a negotiated price available only to GTIA members.
What Assured Members Gain
ITSPs that have reached Assured status describe benefits that reach well beyond a badge.
Policies and processes that work together. Jim Harryman, founder and CEO of Kinetic Technology Group, found alignment gaps his team had never spotted. “One thing I didn’t expect was for our policies and process to not line up. Before the Trustmark, we didn’t realize it.”
A security-first culture. Michael Yudovin, senior engineer and CTO at Reliable Technology, saw his whole team shift. “There’s always something and now our culture is different. People operate within guard rails.”
Faster trust with clients. Alvaka Networks used the Trustmark to cut the time it took to win one client from multiple hours to 10 minutes. “The Trustmark has created a clear differentiator for us in the marketplace and led to closing new business,” said Kevin McDonald, COO and CISO.
Proof that you lead by example. Kevin Mann, president of Resilient IT, pursued the Trustmark to show clients how security is done. “I want to be a company demonstrating those requirements. It’s a market differentiator.”
What the Journey Takes
Achieving the Trustmark takes focused effort, and members who have done it say the investment pays off. Most companies are ready for their initial assessment within 10 months. Organizations starting without documented policies should plan for 12 to 18 months, with 2 to 5 hours of work each week.
Assured members offer this advice for a smooth path:
- Put it on the calendar. “Don’t boil the ocean. Do little steps at a time. But absolutely, dedicate time to this. Put it on the calendar,” said Yudovin.
- Bring your whole team in. “I realized I had to include everyone in this journey,” said Carmine Corridore, president and founder of Underdog Cyber Defense.
- Write policies that fit your business. Mann recommends crafting policies around your own technology, stack and culture so they work in daily practice.
- Plan for continuous improvement. Trustmark holders are assessed annually, so your security posture keeps maturing year after year.
Show Clients the Proof
GTIA gives every participant a badge that reflects their stage in the program: In Progress, Provisional or Assured. You can show clients and prospects your commitment from day one. Assured Trustmark holders also receive a marketing toolkit, including a press release template, to share the achievement publicly. “We presented it to several large clients, and they have increased confidence in us,” one Assured organization reported.
Frequently Asked Questions
Who can join the GTIA Cybersecurity Trustmark Readiness Program? The Readiness Program is open exclusively to GTIA members. Joining also requires a small program fee and a subscription with an approved governance, risk and compliance (GRC) vendor.
How long does it take to earn the GTIA Cybersecurity Trustmark? Most companies are ready for their initial assessment within 10 months. Organizations starting without documented policies should plan for 12 to 18 months as 2 to 5 hours per week.
What frameworks is the GTIA Cybersecurity Trustmark based on? The Trustmark is foundationally based on CIS.
How long does the GTIA Cybersecurity Trustmark last? Trustmark holders are assessed annually, which keeps their status current and their security posture maturing.
Start Your Readiness Journey
You protect your clients every day. The Trustmark shows the world you protect your own business with the same rigor. If you have a mature cybersecurity posture, or you want one, the Readiness Program is your path forward, and it is reserved for GTIA members.
Join the Readiness Program by completing the interest form. Send questions to [email protected].
Keep reading:
- Getting the GTIA Cybersecurity Trustmark (Part 1): Showcasing Your Company’s Security
- Getting the GTIA Cybersecurity Trustmark (Part 2): Lessons from the Trenches
- Getting the GTIA Cybersecurity Trustmark (Part 3): Advice from Assured Members
- Getting the GTIA Cybersecurity Trustmark (Part 4): How to Obtain Employee Buy-In
- The GTIA Cybersecurity Trustmark Is Helping MSPs Prove Their Cyber Prowess